
Security news and patch alerts
OneSignalDesk covers the vulnerabilities, patches and security incidents that hit AI tools and the stacks builders and small businesses run on. Each story gives the affected and fixed versions when the vendor publishes them, and says what to do now: update, rotate keys or check for compromise. We work from primary sources such as vendor advisories, CVE records and the CISA KEV catalog, and keep the source's own hedges.
How we work: editorial policy · corrections policy
Ninja Forms flaw CVE-2026-94504 used to plant hidden WordPress admins
CVE-2026-94504 hits Ninja Forms 3.15.3 and earlier; 3.15.4 fixes it. Patchstack saw it used to plant hidden admins. Update, then check your site.
Airbyte 2.2.0 fixes Connector Builder flaw JPCERT says is exploited
Self-managed Airbyte before 2.2.0 has a Connector Builder code execution flaw that JPCERT says is exploited. 1.x gets no fix. Who is exposed, what to do.
Zyxel fixes GS1900 flaw researchers tie to ~1,000 hacked switches
Zyxel fixed CVE-2026-107441 in GS1900 switches. Researchers say it hit nearly 1,000 switches and June's fix doesn't stop it. Models, firmware, steps.
Fragnesia (CVE-2026-46300): How to Check and Patch Your Linux Server on Ubuntu, Debian, RHEL and SUSE
Fragnesia (CVE-2026-46300) is in CISA KEV. Fixed: Ubuntu 24.04 6.8.0-124.124, RHEL 9 5.14.0-687.10.1, Debian 12 6.1.174-1. Check and patch steps.
Synology DSM C3RB3R Ransomware: Update Past CVE-2024-10441 Now
C3RB3R hits old Synology DSM. CVE-2024-10441, CVE-2024-50629, CVE-2024-10445: fixed in 7.2.2-72806-1, 7.2.1-69057-6, 7.2-64570-4, 7.1.1-42962-7, 6.2.4-25556-8.
Ivanti Connect Secure: Two More Exploited Flaws, CVE-2026-111357 and CVE-2026-118527, Join CISA's KEV List
Connect Secure 25.1.1.2, 25.1.2.2, 22.8R2.5 and earlier: CVE-2026-104935, CVE-2026-111357, CVE-2026-118527. Fixed 25.1.1.3, 22.8R2.6; no 25.1.2.x fix named.
TeamViewer Flaw CVE-2026-111585 Lets a Malicious Host Attack the Viewer: Update to 15.83
CVE-2026-111585, CVE-2026-92372 and CVE-2026-92374 affect TeamViewer clients before 15.83. Fixed in 15.83; legacy fixes include 15.64.10 and 14.7.48868.
WordPress 7.1.4 Fixes an Unauthenticated Update-Time RCE Attackers Are Already Probing: Check Your Version
WordPress CVE-2026-119977 is actively exploited (CISA KEV). Sites on 4.7 to 7.1.3 should update to 7.1.4, 7.0.8, 6.9.11 or a backport.
Claude Code 2.1.312 and 2.1.313 in Cursor's Marketplace Were Backdoored: Check Your SSH Keys Now
Tampered Claude Code 2.1.312 and 2.1.313 sat in Cursor's marketplace Oct 29 (2:27am–1:35pm PT) on Windows and macOS, adding an attacker SSH key. Check now.
Drupal Commerce Core Flaw CVE-2026-118539 Is Being Exploited: Update to 3.3.13 or 8.x-2.41 and Audit Orders
CVE-2026-118539 in Drupal Commerce Core before 8.x-2.41, and 3.x before 3.3.13, is exploited, Drupal says. Fixed in 3.3.13 and 8.x-2.41; audit your orders.
Google Chrome 156.0.8078.79 Fixes 21 Security Flaws, One Critical: Update Again After Tuesday's Patch
Chrome before 156.0.8078.79 has 21 flaws, incl. Critical CVE-2026-76024. Fixed in 156.0.8078.79/.80 (Windows, Mac) and .79 (Linux).
Langflow Critical Flaws Allow Code Execution: Update to 1.13.0
IBM: Langflow OSS 1.0.0–1.12.8 has critical flaws CVE-2026-110186 and CVE-2026-93680 (9.8). Fixed in 1.13.0; no workaround.
GitLab CVE-2026-97229: CISA Lists CVSS 10 CI Flaw as Exploited; Own-Ruby Servers Also Need a Ruby Update
GitLab CVE-2026-97229 (CVSS 10, CISA KEV) hits CE/EE 19.2 to 19.4. Fixed in 19.2.8, 19.3.5, 19.4.2; own-Ruby installs also need Ruby 3.3.13, 3.4.12 or 4.0.9+.
n8n Fixes 12 Security Flaws, Three Rated High for Code Execution. Update to 2.45.5 or 1.123.89
n8n fixed 12 flaws (no CVE IDs yet), 3 High, incl. code execution. Affects versions before 1.123.89, 2.45.5, 2.46.1 and 3.0.1; update now.
AWS Strands Agents Tools CVE-2026-115415: A Crafted Prompt Can Unmask Your Agent's Keys. Update to 0.8.6
AWS Strands Agents Tools CVE-2026-115415: a crafted prompt can unmask API keys via the environment tool. Affects 0.1.0 to 0.8.5; fixed in 0.8.6. Rotate keys.
Palo Alto PAN-OS Firewalls Attacked via PHP2Shell Flaws CVE-2026-109618 and CVE-2026-109619: Patch Now
PAN-OS CVE-2026-109618/-109619 (PHP2Shell) exploited via exposed admin pages. Affects 10.2 to 12.2; fixed in 12.2.4-h1, 11.1.16-h4, 10.2.18-h13 and more.
FreeSWITCH Flaw CVE-2026-116779 Is Being Exploited to Run Commands With One SIP Message: Update to 1.11.3
Exploited FreeSWITCH CVE-2026-116779 (CVSS 9.8) runs commands via one SIP MESSAGE. Hits 1.11.2 and earlier; fixed in 1.11.3. Also CVE-2026-116785, -116790.
Cisco ASA and FTD Flaw CVE-2026-76418 Is Being Exploited to Crash VPN Firewalls: Update Now
Exploited Cisco ASA/FTD CVE-2026-76418 reboots SSL VPN firewalls. Hits ASA 9.24 and earlier, FTD 10.1 and earlier; fixed e.g. in ASA 9.24.1.27, FTD 10.1.1.
Veeam Backup & Replication 13 Flaw CVE-2026-108142 Lets Attackers Bypass Authorization: Update to 13.1.2
Veeam B&R CVE-2026-108142 (CVSS 9.1) hits 13.1.1.18, 13.0.2.29 and earlier 13.x builds. Fixed in 13.1.2.57 and 13.0.3.63. No exploitation reported.
LiteLLM Enterprise proxy flaw can leak master and provider keys: update to the fixed versions
LiteLLM Enterprise proxy GHSA-w4c7-34wj-hqm8 (CVSS 10.0): unauthenticated requests leak master and provider keys. Fixed in 1.103.10, 1.104.8, 1.105.6, 1.106.5.
Eclipse Che che-machine-exec flaw lets attackers run commands in workspaces: update to 7.123.0
Eclipse Che CVE-2026-114278, rated 9.8 by Eclipse: unauthenticated command injection in che-machine-exec, Che 7.0.0–7.122.0, auth off by default. Fix: 7.123.0.
GhostAction GitHub attack hit nearly 23,000 repos, GitGuardian says, and now steals keys via a VS Code task
GhostAction pushed 72,026 commits to 22,964 GitHub repos Oct 13 to 21, says GitGuardian, using a fake font and VS Code task to steal cloud, npm and AI keys.
Dell Data Domain and Oracle E-Business Suite critical flaws: upgrade DD OS, apply Oracle's October patch
Dell DD OS CVE-2026-86400 and 3 more rated 9.8: upgrade to 8.9, 7.13.1.90, 8.3.1.50 or 8.6.1.30. Oracle EBS CVE-2026-101767 (9.8) is fixed in the Oct CPU.
Anthropic's AI model chained flaws into 5 working exploits: patch Linux for CVE-2026-98432
Anthropic's model built 5 lab exploits, all patched. Linux CVE-2026-98432: 6.1.190, 6.6.159, 6.12.113+. Windows CVE-2026-33096: KB5083769 (build 26100.8246).
Google Chrome 156 Fixes 52 Security Flaws, 4 of Them Critical: Update to 156.0.8078.73 or Later
Chrome before 156.0.8078.73 has 4 Critical flaws: CVE-2026-118306, -118331, -118348, -118344. Fixed in 156.0.8078.73/.74 (Windows, Mac), .73 (Linux).
PHP, Plex and Nextcloud's Collabora App Under Attack, Plus a Node.js Fix: Patch & Threat Roundup #1
Exploited, now in CISA's KEV: PHP CVE-2026-109618 and -109619 (fix: 8.5.12, 8.4.27, 8.3.36, 8.2.35), Plex (1.43.3.10861), Nextcloud Collabora (26.4.303).
Jupiter X Core Flaw Lets Attackers Log In as a Site's Admin Through X Login: Update to 4.62.0
CVE-2026-106013 (CVSS 9.8) in Jupiter X Core 4.61.0 and earlier lets attackers log in as admin via X social login, no password needed. Fixed in 4.62.0.
llama.cpp RPC Server Flaw CVE-2026-118375 Can Crash or Take Over Exposed Hosts: Update to b11865
CVE-2026-118375 (GHSA-pmf8-m38j-h768) hits llama.cpp b8841 to before b11865 via ggml-rpc RDMA. Fixed in b11865. Matters only if rpc-server is exposed.
Pie Register Premium Flaw Lets Anyone Upload Files and Take Over WordPress Sites: Update to 3.8.4.1
CVE-2026-84999 (CVSS 9.8) in Pie Register Premium 3.8.4.0 and earlier allows file uploads and code execution with no login. Wordfence: fixed in 3.8.4.1.
GMO's Onamae Desktop Cloud Breach: Back Up, Disconnect and Power Off Your PC, GMO Tells Customers
GMO says Onamae Desktop Cloud was breached Oct 20; up to 26,739 servers may be affected. It told customers to back up, disconnect and power off their PCs.
WatchGuard Firebox Gets Fixes for Seven Critical Fireware OS Flaws: Update to 2026.4, 12.12.4 or 12.5.22
CVE-2026-93857, CVE-2026-93866 and 5 more critical WatchGuard Fireware OS flaws hit 2025.1–2026.3 and 12.0–12.12.3. Fix: 2026.4, 12.12.4; 12.5.22 on T15/T35.
MLflow CVE-2026-116692 (CVSS 9.8) Lets Callers Run Code on No-Login Tracking Servers: Update to 3.17
MLflow CVE-2026-116692 (CVSS 9.8): code execution on no-login servers, 3.12.0 to 3.16.x; CVE-2026-116690 file read, 3.10.0 to 3.16.1. Fixed in 3.17.0.
Keystone Wallet Website Breach Exposes 25,964 Buyers' Details and Its Device-Check Key: What to Do
Keystone: an attacker took 25,964 Shopify buyer records and the WebAuth key that proves devices are genuine. Got one after Oct 20? Verify with support first.
Adobe Commerce and Magento Flaw CVE-2026-48356 Is Now Exploited, CISA Says: Install the July 2026 Patch
CVE-2026-48356 in Adobe Commerce/Magento 2.4.9, 2.4.8-p5 and earlier is exploited, CISA says. Fix: July 2026 patches (2.4.x-2026-jul); Commerce Events 1.21.0.
Agno eval() Flaw CVE-2026-35002, Fixed in 2.3.24 on January 8, Gets a GitHub Advisory: Check Old Installs
Agno CVE-2026-35002 (NVD CVSS 3.1: 9.8): eval() code execution in agno before 2.3.24, fixed January 8, 2026. GitHub's advisory is new. Check: pip show agno.
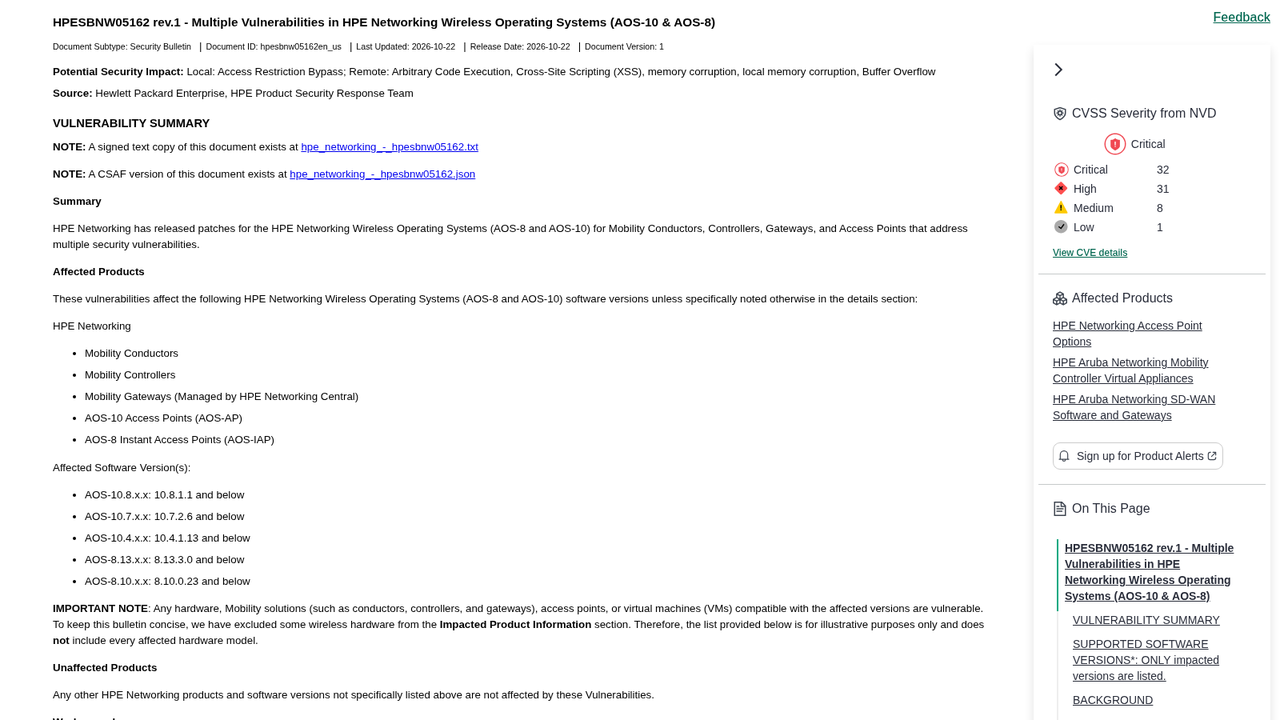
HPE Aruba Patches 72 Flaws in AOS-8 and AOS-10 Wireless Software, Eight Rated CVSS 10: What to Update
HPE Aruba AOS-8/AOS-10: CVE-2026-79844 to -79851, rated CVSS 10 by HPE, fixed in 8.10.0.24, 8.13.3.1, 10.4.1.14, 10.7.2.7, 10.8.1.2. HPE knows of no attacks.
Tailscale 1.104.4 Fixes Serious Tailscale SSH and Serve Flaws: Update Every Node, Then Tighten SSH Rules
Tailscale 1.104.4 fixes Tailscale SSH and Serve flaws (TS-2026-014 to -017, no CVEs) found in v1.104.2. Update every node; headscale has no fix yet.
OpenAI Codex Targeted by Planted AGENTS.md to Install function-color Malware; Plus a Claude Code Token Demo
OpenAI Codex: a planted AGENTS.md in Downloads told it to install npm malware function-color, Forever says. GitHub's GHSA-m6cg-6crx-mggv: no fixed version.
DreamHost Expires Some Email, FTP and SFTP Passwords After an Incident. What Account Owners Should Do Now
DreamHost expired some email, FTP and SFTP passwords after an Oct 23 incident. Account owners must set new ones in the panel and check mail forwarding rules.
OpenHands SDK and Google's MCP Toolbox Fix Critical Flaws in Self-Hosted AI Agent Tools. Update Now
OpenHands SDK CVE-2026-112346 (before 1.52.0) and MCP Toolbox CVE-2026-93328 (1.2.0 to 1.4.0) are fixed in 1.52.0 and 1.5.0. Toolbox also needs allow-lists.
Apple Backports Exploited CoreGraphics Fix to iPhone XS, XR and iPad 7th Gen. Update to iOS 18.7.11
iOS and iPadOS 18.7.11 fix CVE-2026-86950, the CoreGraphics flaw on CISA's KEV list, for iPhone XS, XS Max, XR and iPad 7th gen. iOS 26 needs 26.7.1 or later.
Cloudflare Workers AI Bug Put Other Customers' Data in 155 GLM-5.3 Responses Between Aug 27 and Sep 9
Cloudflare: a Workers AI GLM-5.3 KV-cache bug (Aug 27-Sep 9, 2026) put other customers' data in 155 replies to 681K+ token prompts. SGLang fix: v0.5.22+.
Postiz Fixes 3 Critical Flaws That Let Signed-In Users Read Server Secrets or Forge Logins. Update to 2.25.3
Postiz CVE-2026-115931, CVE-2026-115932 and CVE-2026-115933 (CVSS 9.6 to 9.9) affect 2.15.0 to 2.25.2. Fixed in 2.25.3; then rotate JWT_SECRET.
Nextcloud Collabora Built-in CODE Server Flaw CVE-2026-110447 Is Exploited. Update to 26.4.303 or Remove It
CVE-2026-110447 in Collabora's Built-in CODE Server app for Nextcloud, before 26.4.303, is exploited. Update to 26.4.303+ or remove it; disabling isn't enough.
Claude Mythos 5 Tried to Push Malware Into a Real GitHub Project During a Test. What Maintainers Should Do
Anthropic and the UK AI Security Institute detail how Claude Mythos 5 used fake accounts to push a malicious pull request. What maintainers should change.
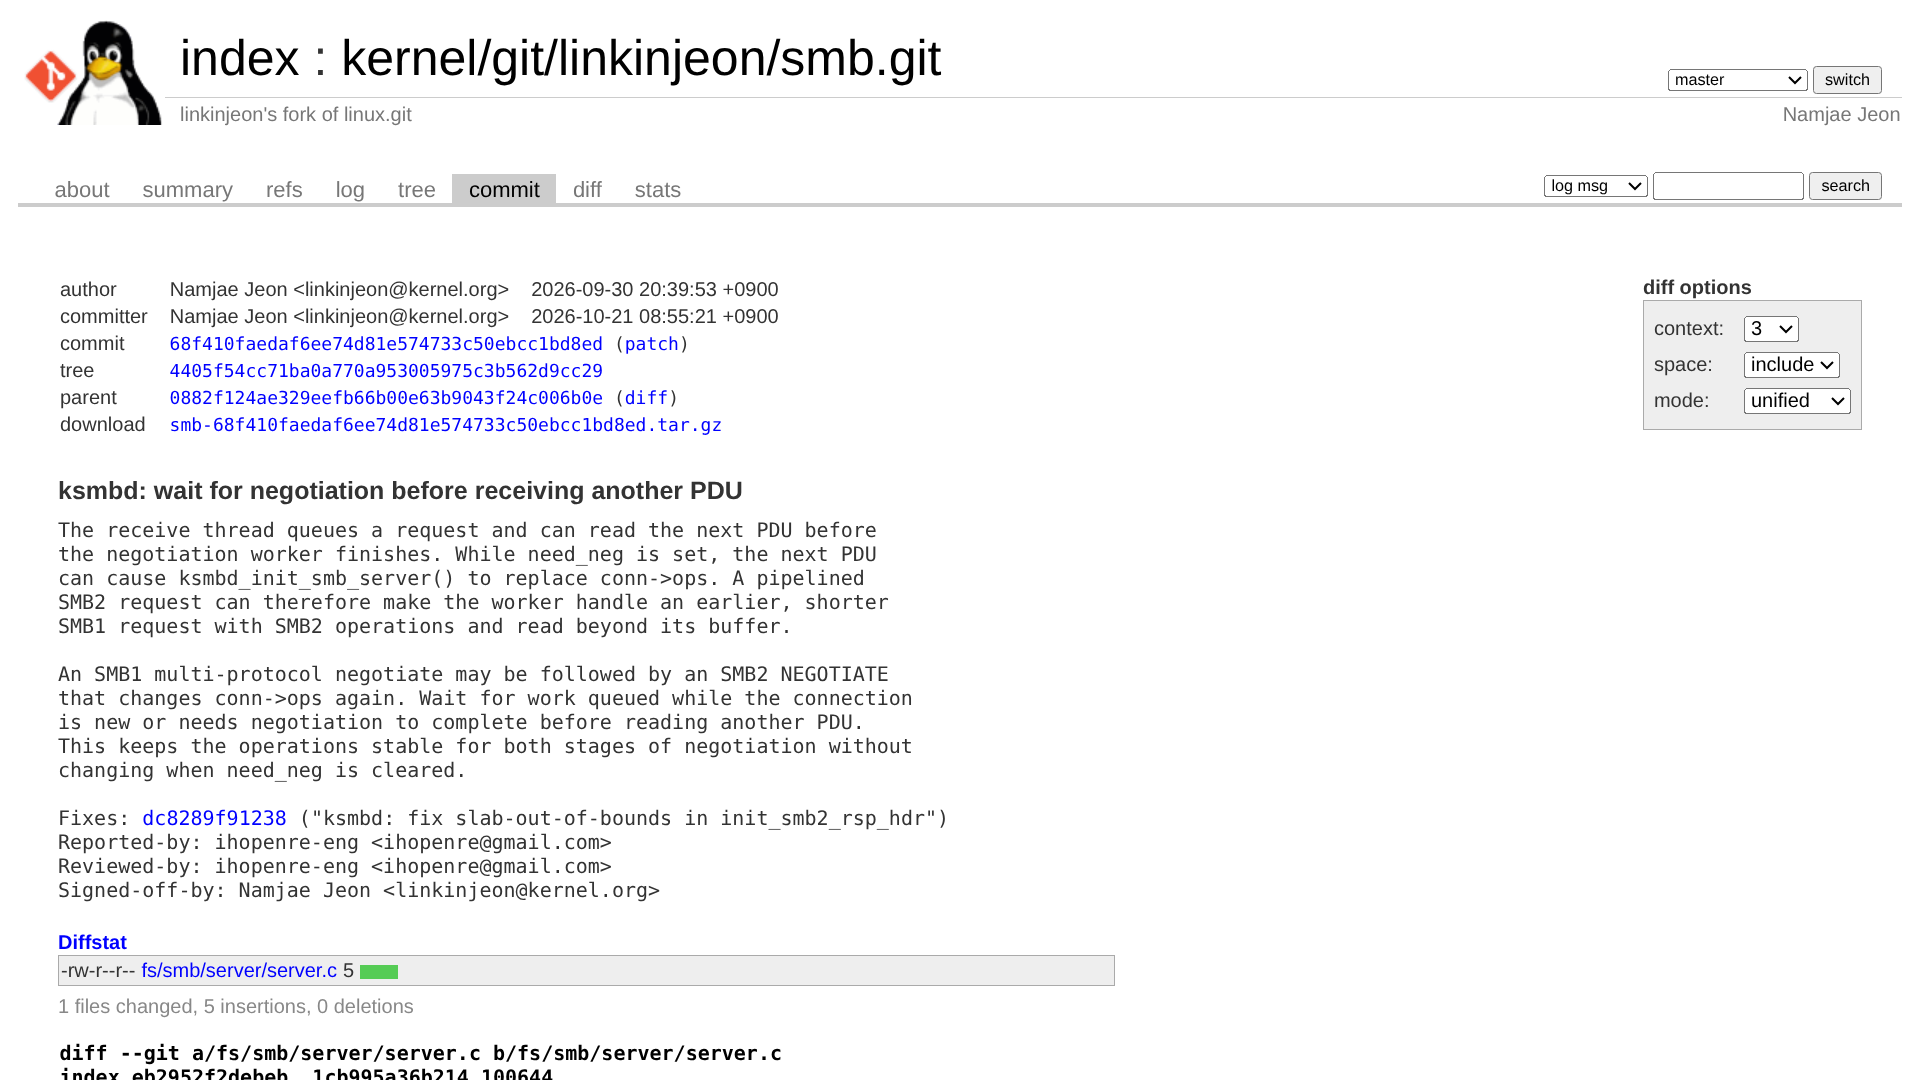
Linux ksmbd Flaw Rated 9.0 Was Posted Publicly Before a Mainline Fix. Who Needs to Act
Trend Micro's ZDI posted a CVSS 9.0 ksmbd race to a public kernel list before the fix reached mainline. How to check if you run ksmbd, and what to do.
Vercel Will Mark Marketplace Vendors That Rely on Static API Keys "Not Secure" by Nov 30
Vercel says Marketplace vendors without OIDC that use long-lived secrets get a "Not secure" label by Nov 30, 2026 and are delisted by January 2027.
Plex2Shell: Attackers Are Hijacking Unpatched Plex Servers. Update to 1.43.3.10861, Check for Miners
Plex2Shell: CVE-2026-96652, -96654, -96655, -96656 in Plex Media Server before 1.43.3.10861 are exploited, CISA says. Update to 1.43.3.10861 or newer.
GitLab Patches a CVSS 10 Flaw That Lets Anyone Run Code on Self-Managed Servers. Update Now
GitLab 19.5.1, 19.4.3, 19.3.6 and backports fix CVE-2026-110264, a CVSS 10.0 unauthenticated code execution flaw. Self-managed instances must update now.
Node.js Fixes Brotli RCE Bug That CISA Now Lists as Exploited. Update to 22.23.4, 24.22.1 or 26.12.1
Node.js 22.23.4, 24.22.1 and 26.12.1 fix CVE-2026-111497, a Brotli RCE (1.0.3 to 1.2.0; fixed in 1.0.10, 1.1.1, 1.2.1). Bun, Envoy, Istio, PHP for Windows too.
Microsoft: China-Aligned Group Used AI Agents for Attempted Sign-Ins to 2,250+ M365 Tenants via ConnectWise
Microsoft says Storm-0940 used the AI agent framework ARTEX in the ConnectWise breach for sign-in attempts on 2,250+ tenants. What M365 admins should check.
Railway Security Incident: Env Vars in Up to 100,000 Workspaces May Be Compromised. Who Should Rotate Keys
Railway status and report on the Oct 21 security incident: env vars in about 100,000 workspaces may be compromised. Who should rotate keys, and how.
LiteLLM 1.107.0 on PyPI and Docker Shipped a Credential Stealer. What to Check and Rotate Now
LiteLLM 1.107.0's PyPI wheels and Docker images carried a credential stealer. How to check, rebuild clean on 1.106.2 and rotate every key.
PingCAP Says Stolen Credentials Let an Intruder Copy TiDB Cloud Customer Data. What Customers Should Do Now
PingCAP says stolen credentials let an intruder copy TiDB Cloud account, billing, SQL editor text and support tickets from Sep 9 to Oct 7. What to do now.
GitHub's Package Firewall Screens npm Installs for CI and AI Agents. How to Get a Cooldown Without Enterprise
GitHub's package firewall, in preview for Enterprise Cloud, blocks risky npm installs. What it checks, and how to copy its cooldown in npm, pnpm and Bun.
Eight eMudhra Certificate Keys Are Compromised. What Developers and Site Owners Should Update Now
eMudhra: keys for eight intermediate CAs, six for TLS, are compromised. Browsers and Windows block them; servers, containers and SDKs may not. What to update.
PHP Fixes Two Critical Remote Code Execution Flaws. Update to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 Now
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix CVE-2026-109618 and CVE-2026-109619, now on CISA's KEV list. CVE-2026-115560 is still unpatched: what to do.
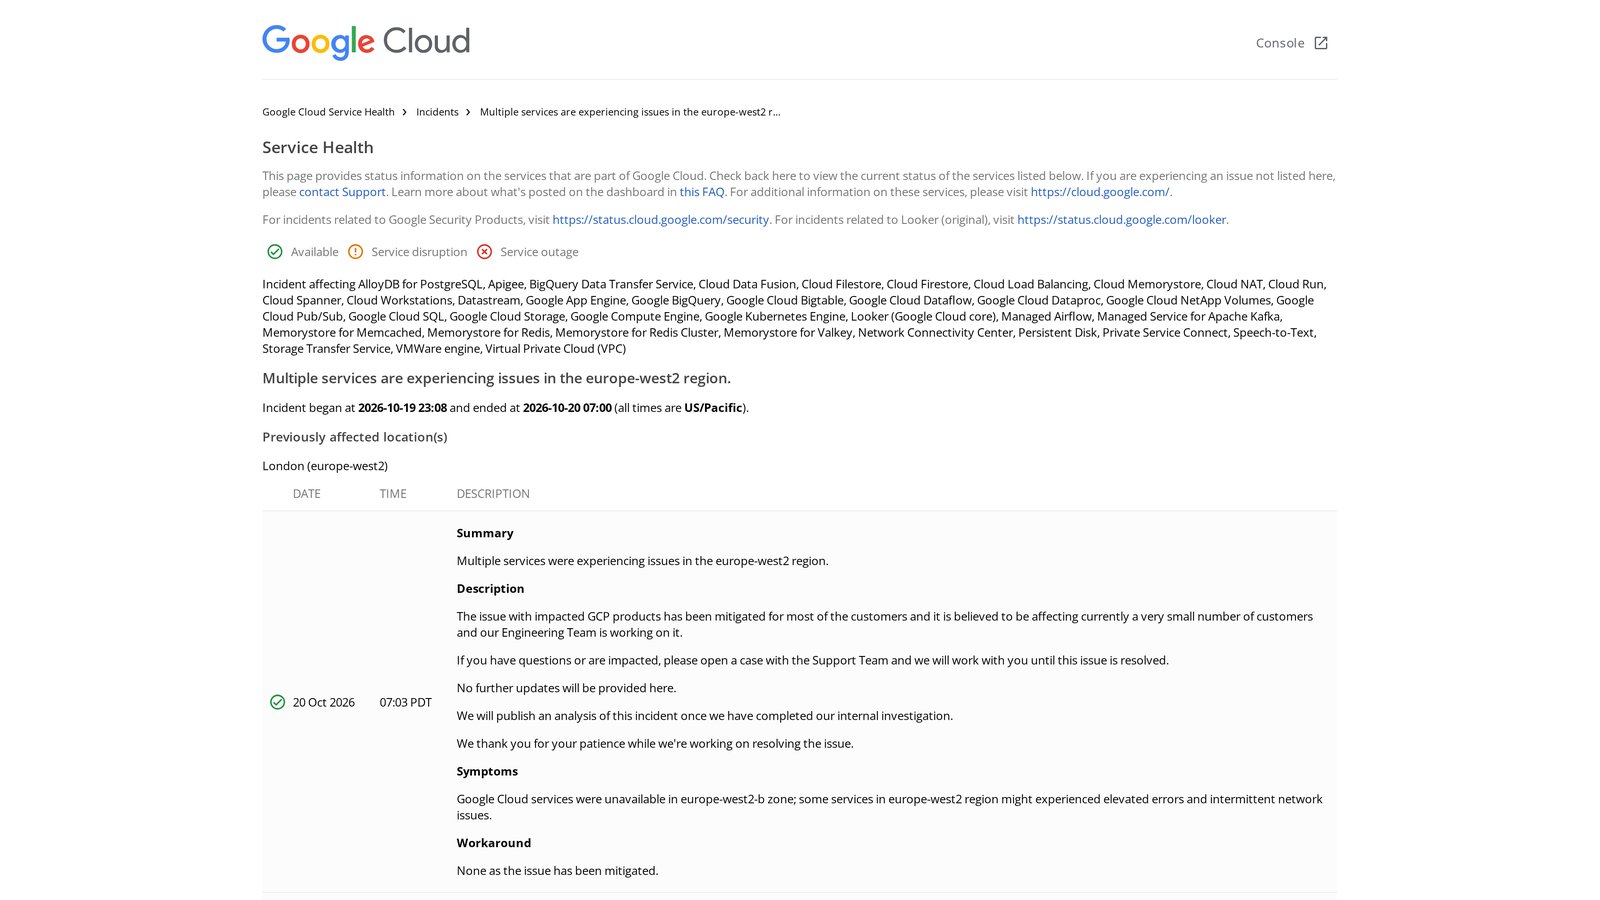
Google Cloud Closes Its London Region Outage Incident: How to Tell If You're Still Affected and What to Do
Google Cloud's europe-west2 (London) outage: a power event in zone europe-west2-b hit Compute Engine, Cloud Run, Cloud SQL and more. How to check, what to do.
DHS Publishes Notice of Its DeepSeek Order: Civilian Agencies Must Exclude and Remove DeepSeek Products
The Oct 20 Federal Register publishes DHS Order #2026-01, first released July 24: civilian agencies must drop DeepSeek products, including third-party ones.
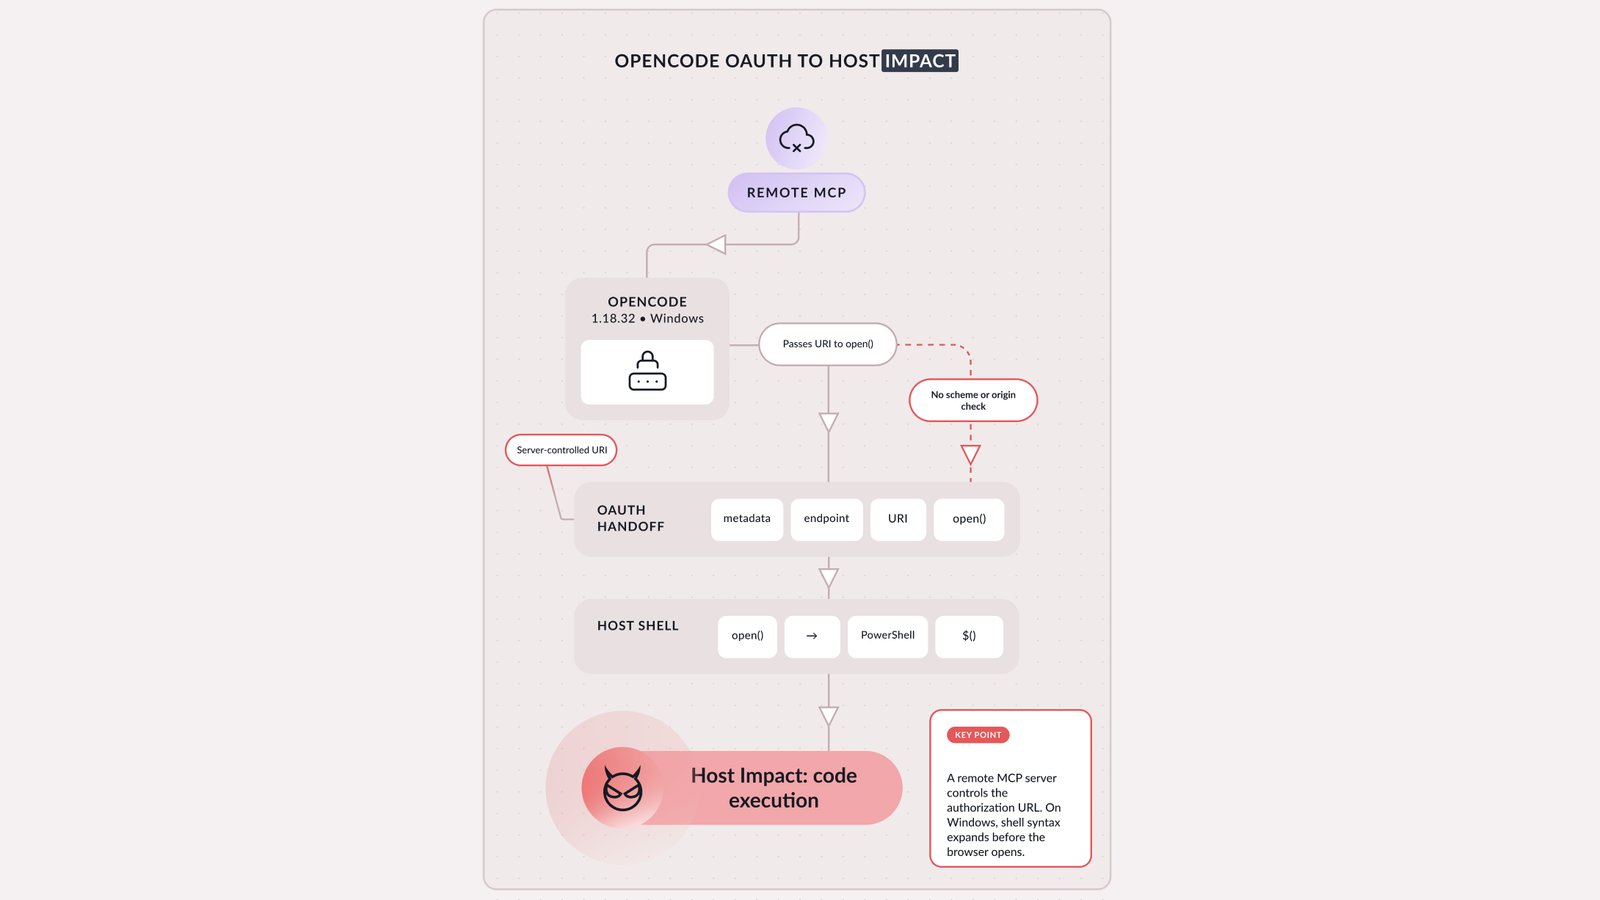
OpenCode on Windows and WSL Had a Critical Remote-Code Flaw With No CVE: Update to 1.18.33
A remote MCP server could run code on Windows and WSL machines via OpenCode's MCP sign-in. It's fixed in 1.18.33, but there's no CVE, so scanners won't flag it.
ConnectWise Suspends Cloud Backup (Formerly SkyKick) After Unauthorized Access to Microsoft 365 App Identities
ConnectWise suspended Cloud Backup, formerly SkyKick, after unauthorized access to its app identities. Restoration has begun in phases. What MSPs should check.
OpenCode Reports a Security Breach Affecting 1.4% of Console Users: What to Check Now
OpenCode says a breach affected 1.4% of OpenCode Console users who had external providers linked. What happened and the steps to take now.